KNIME AP Secrets Retriever gets secret file from Hub and stores it locally
I’m concerned about the security implications for how files stored in the Hub secrets store are handled locally by KNIME AP. My findings are as follows - can someone please alleviate my concerns or understanding, or is this an actual risk?
To reproduce:
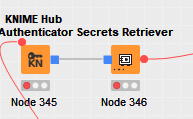
I dutifully placed a key (p8 file) in KNIME Hub’s secrets. I then used a KNIME Hub Authenticator in my AP workflow to authenticate to KNIME Hub, and connected that to a Secrets Retriever node (screenshot).
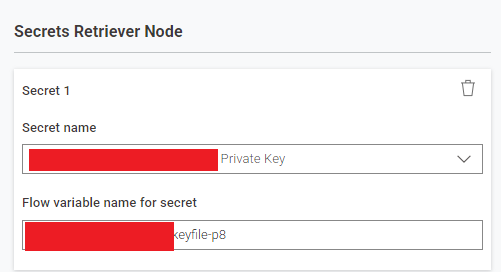
The Secrets Retriever node is configured to pull that p8 file (screenshot).
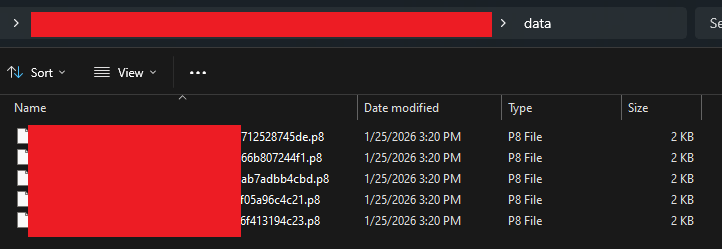
When it executes, the p8 file is written to the workflow’s data area (screenshot) on the local machine, and is readable. A portion of the name of the file to the write is slightly altered with several hex numbers, but the portion on the left matches e.g.
this_is_my_secret_keyfil324cef5ded5f4121.p8When the Secrets Retriever node resets, the p8 file disappears. When I close the workflow, the p8 file also disappears.
However, KNIME AP:
1.
Does write the file to the LOCAL repo on the local disk, which makes it potentially accessible by other processes.
1.
Cannot clean up after itself properly in case it crashes. This can leave files accessible indefinitely. This is how I noticed the issue.
Per the Secrets Guide webpage, the secrets are not stored when it is saved for security reasons, but p8 files appear locally regardless of whether the workflow is saved.